Nearly 800 Malicious npm Packages Deliver Cross-Platform RAT and Infostealer
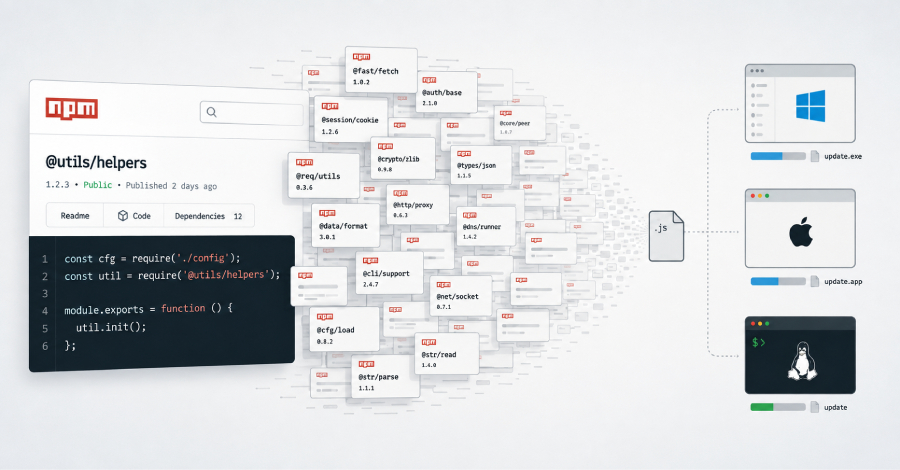
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targeting Windows, Mac, and Linux systems. “These packages appear to use AI slop squatted, or randomly...
ClickFix Attacks Deliver macOS Stealer That Can Drain Crypto Wallets
ClickFix-style attacks are being used to deliver a Go-based malware capable of stealing cryptocurrency assets, as well as browser-stored passwords, Apple iCloud Keychain data, and cached credentials. The macOS-focused infection chain is designed to deliver a shell...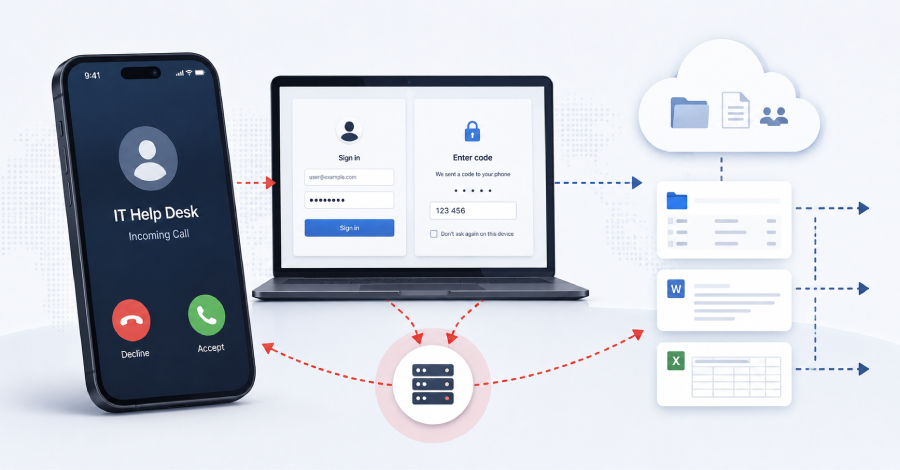
UNC6671 Vishing Attacks Target Personal Phones to Steal SaaS Data
A recent wave of cyber attacks targeting financial services, private equity, and professional services is attributed to a data extortion group known as UNC6671. “UNC6671 continues to rely on voice phishing (vishing) to target enterprise employees, posing as IT...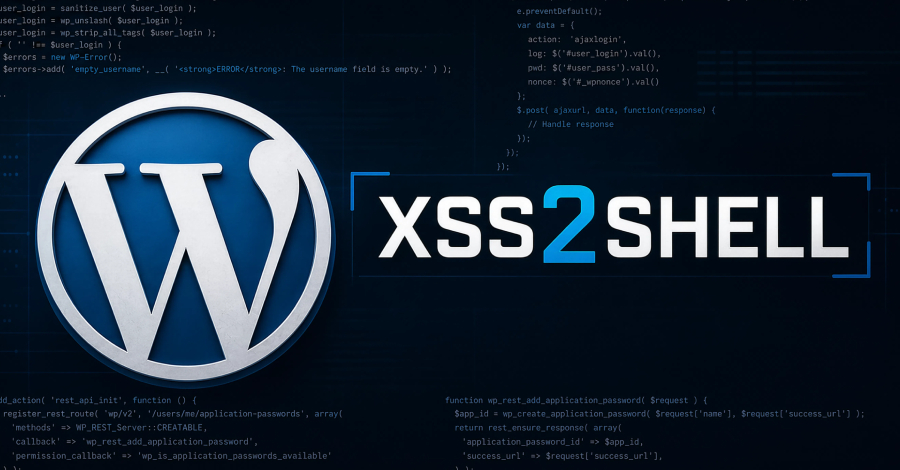
New WordPress Pre-Auth XSS Could Lead to PHP Code Execution – Patch ASAP
WordPress has fixed a pre-authentication reflected cross-site scripting (XSS) flaw in its login screen that affects every version of the content management system. Under additional conditions, the bug can be chained into PHP code execution on the server. Tracked...
About Us
CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.