
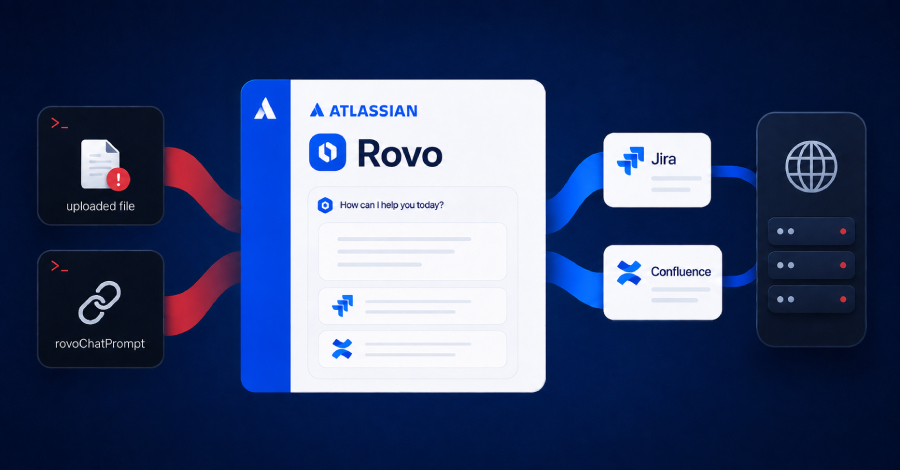
Atlassian Rovo Can Be Tricked Into Sending Jira and Confluence Data to Attackers
Attacker-controlled instructions can make Atlassian’s Rovo assistant collect Jira or Confluence data that a signed-in user can access, then send it to an outside server. Two security firms found that behavior independently, by different routes. Only one of those...
New CSS Attacks Can Break Webmail Defenses to Steal Passwords and Tokens
New research shows content inside an email can escape its message boundary and interfere with the webmail interface. Across attack chains spanning Outlook, Gmail, Fastmail, Proton Mail, Yahoo Mail, and AOL Mail, the techniques can capture passwords, take over...
Metabase Zero-Day Exploited in Wild Allows Admin Access Without Authentication
Metabase has warned that a maximum-severity security flaw impacting its business intelligence and data visualization software package has been exploited in the wild as a zero-day. The vulnerability (CVSS score: 10.0), which does not carry a CVE identifier, allows an...
N-able Issues N-central Hotfix 2 as Attackers Reach Managed Systems and Persist
N-able has released a fresh round of hotfixes for N‑central as part of its investigation into ongoing exploitation of a recently disclosed security flaw in the Remote Monitoring and Management (RMM) product. “We are proactively expanding protections in response...
About Us

CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.
