
DOUBLECUP Uses ClickFix and Cached PNGs to Deliver CountLoader and DeviceManager RAT
A new Russian loader-as-a-service (LaaS) codenamed DOUBLECUP has been using ClickFix lures as a way to stage malware-laced PNG images in victims’ browser cache and ultimately deliver CountLoader and a previously undocumented remote access trojan called...
CISA Adds Exploited N-able N-central Flaw to KEV After Customer Compromises
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a high-severity security flaw impacting N-able N-central to its Known Exploited Vulnerabilities (KEV) catalog following reports of active exploitation in the wild. The vulnerability,...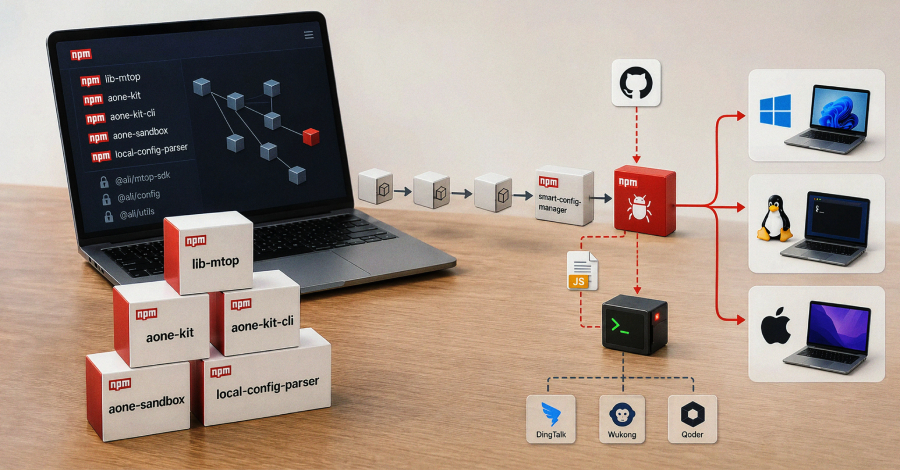
18 Malicious npm Packages Deliver Cross-Platform RAT to Alibaba Tool Users
Cybersecurity researchers have discovered a new set of malicious npm packages that target users of Alibaba developer tools with a cross-platform remote access trojan (RAT) as part of a sophisticated, targeted software supply chain attack targeting Chinese-speaking...
Google Password Manager Attacks Could Let Malware Hijack Passkey-Protected Accounts
Malware running as an ordinary user on a Windows machine can sign into a victim’s passkey-protected accounts without a fingerprint, a PIN, or anything at all appearing on the victim’s screen. Unit 42 detailed three attack paths against Chrome’s...
INC Ransomware Emerges as Dominant Actor Exploiting SonicWall SMA 1000 Flaws
The INC Ransomware operation has emerged as the “dominant threat actor” exploiting the recently disclosed security flaws in SonicWall Secure Mobile Access (SMA) 1000 series VPN appliances. In a report published over the weekend, Resecurity said it observed...
About Us

CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.
