


Researchers Find Exploit Allowing NTLMv1 Despite Active Directory Restrictions
Cybersecurity researchers have found that the Microsoft Active Directory Group Policy that’s designed to disable NT LAN Manager (NTLM) v1 can be trivially bypassed by a misconfiguration. “A simple misconfiguration in on-premise applications can override...
Hackers Hide Malware in Images to Deploy VIP Keylogger and 0bj3ctivity Stealer
Threat actors have been observed concealing malicious code in images to deliver malware such as VIP Keylogger and 0bj3ctivity Stealer as part of separate campaigns. “In both campaigns, attackers hid malicious code in images they uploaded to archive[.]org, a...
Python-Based Malware Powers RansomHub Ransomware to Exploit Network Flaws
Cybersecurity researchers have detailed an attack that involved a threat actor utilizing a Python-based backdoor to maintain persistent access to compromised endpoints and then leveraged this access to deploy the RansomHub ransomware throughout the target network....
Researcher Uncovers Critical Flaws in Multiple Versions of Ivanti Endpoint Manager
Ivanti has rolled out security updates to address several security flaws impacting Avalanche, Application Control Engine, and Endpoint Manager (EPM), including four critical bugs that could lead to information disclosure. All the four critical security flaws, rated...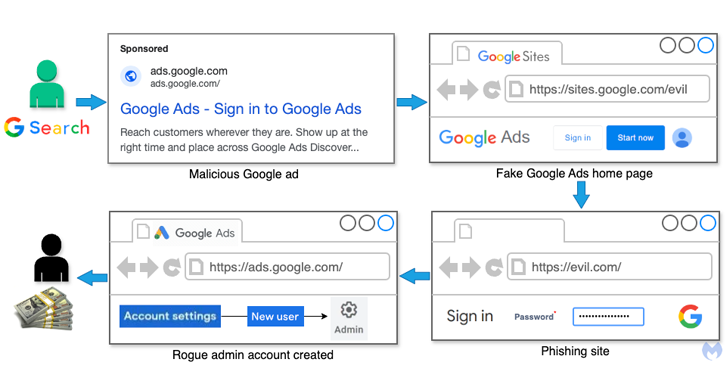
Google Ads Users Targeted in Malvertising Scam Stealing Credentials and 2FA Codes
Cybersecurity researchers have alerted to a new malvertising campaign that’s targeting individuals and businesses advertising via Google Ads by attempting to phish for their credentials via fraudulent ads on Google. “The scheme consists of stealing as many...
About Us

CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.
