APT28 Targets Ukrainian UKR-net Users in Long-Running Credential Phishing Campaign
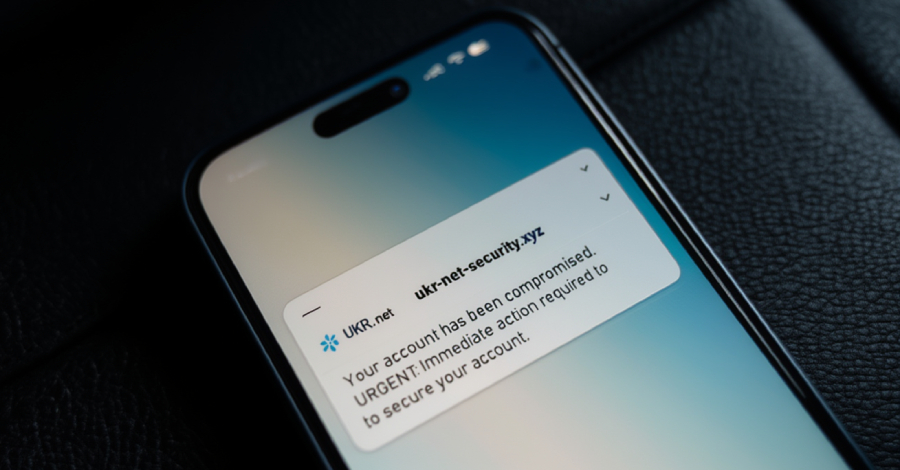
The Russian state-sponsored threat actor known as APT28 has been attributed to what has been described as a “sustained” credential-harvesting campaign targeting users of UKR[.]net, a webmail and news service popular in Ukraine. The activity, observed by...
New ForumTroll Phishing Attacks Target Russian Scholars Using Fake eLibrary Emails
The threat actor linked to Operation ForumTroll has been attributed to a fresh set of phishing attacks targeting individuals within Russia, according to Kaspersky. The Russian cybersecurity vendor said it detected the new activity in October 2025. The origins of the...
Fix SOC Blind Spots: See Threats to Your Industry & Country in Real Time
Modern security teams often feel like they’re driving through fog with failing headlights. Threats accelerate, alerts multiply, and SOCs struggle to understand which dangers matter right now for their business. Breaking out of reactive defense is no longer optional....
China-Linked Ink Dragon Hacks Governments Using ShadowPad and FINALDRAFT Malware
The threat actor known as Jewelbug has been increasingly focusing on government targets in Europe since July 2025, even as it continues to attack entities located in Southeast Asia and South America. Check Point Research is tracking the cluster under the name Ink...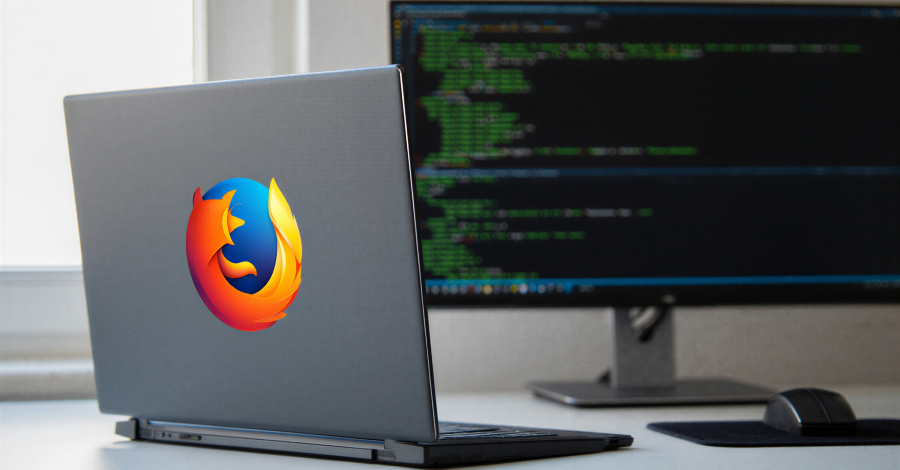
GhostPoster Malware Found in 17 Firefox Add-ons with 50,000+ Downloads
A new campaign named GhostPoster has leveraged logo files associated with 17 Mozilla Firefox browser add-ons to embed malicious JavaScript code designed to hijack affiliate links, inject tracking code, and commit click and ad fraud. The extensions have been...
About Us
CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.