
Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal
A malicious npm package named “indexed-btree” has been observed hiding its malicious behavior within application code rather than using lifecycle scripts, indicating that threat actors are likely shifting tactics in response to recent security controls....
SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-Phishing
The threat actor known as SideCopy has been observed using spear-phishing lures to target academic institutions in India, expanding their strategic focus beyond government entities. “SideCopy campaign operations typically initiate through spear-phishing...
One Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a Backdoor
Malware already running on a Mac can quietly take over Meta’s Muse assistant and use the broad access its owner granted the app, security researcher Patrick Wardle has shown in a proof-of-concept released on September 21. It works by changing a hidden setting so...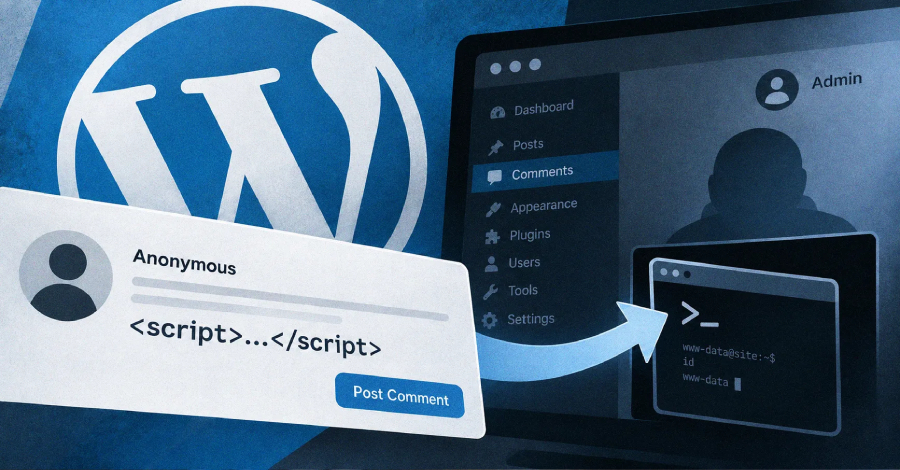
WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session
A new flaw in WordPress core let an anonymous visitor leave a comment that planted a hidden script on the page. If a logged-in administrator later opened that page, the script could run code on the site’s server. WordPress fixed the flaw, tracked...
Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a now-patched security flaw impacting Zyxel GS1900 series switches to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerability, tracked...
About Us

CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.
