NGate Campaign Targets Brazil, Trojanizes HandyPay to Steal NFC Data and PINs
Cybersecurity researchers have discovered a new iteration of an Android malware family calledNGate that has been found to abuse a legitimate application called HandyPay instead of NFCGate. “The threat actors took the app, which is used to relay NFC data, and...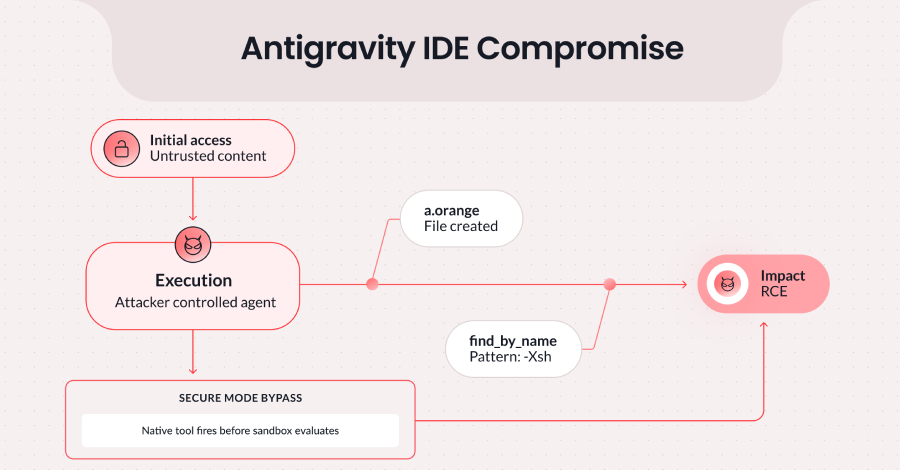
Google Patches Antigravity IDE Flaw Enabling Prompt Injection Code Execution
Cybersecurity researchers have discovered a vulnerability in Google’s agentic integrated development environment (IDE), Antigravity, that could be exploited to achieve code execution. The flaw, since patched, combines Antigravity’s permitted file-creation...
CISA Adds 8 Exploited Flaws to KEV, Sets April-May 2026 Federal Deadlines
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added eight new vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including three flaws impacting Cisco Catalyst SD-WAN Manager, citing evidence of active exploitation. The...
SGLang CVE-2026-5760 (CVSS 9.8) Enables RCE via Malicious GGUF Model Files
A critical security vulnerability has been disclosed in SGLang that, if successfully exploited, could result in remote code execution on susceptible systems. The vulnerability, tracked as CVE-2026-5760, carries a CVSS score of 9.8 out of 10.0. It has been described as...
⚡ Weekly Recap: Vercel Hack, Push Fraud, QEMU Abused, New Android RATs Emerge & More
Monday’s recap shows the same pattern in different places. A third-party tool becomes a way in, then leads to internal access. A trusted download path is briefly swapped to deliver malware. Browser extensions act normally while pulling data and running code. Even...
About Us
CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.