Ghost CMS CVE-2026-26980 Exploited to Hijack 700+ Sites for ClickFix Attacks
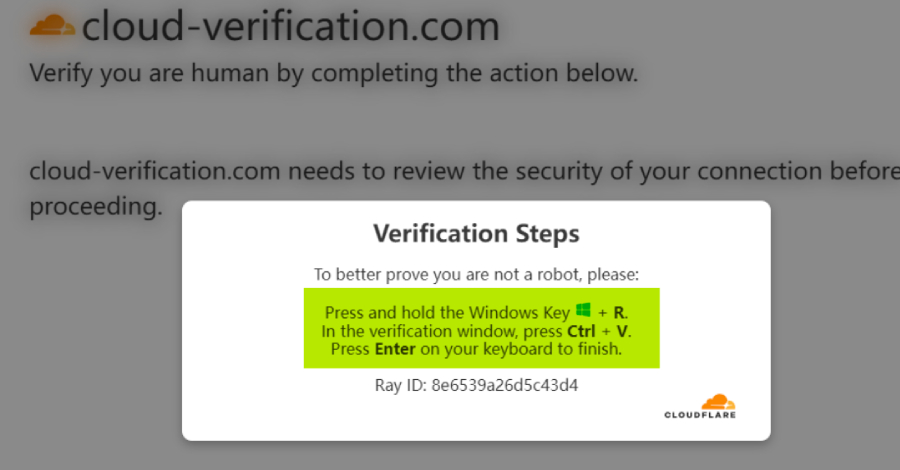
Threat actors are exploiting a recently disclosed critical security flaw in Ghost CMS to inject malicious JavaScript code with an aim to fuel ClickFix attacks. According to QiAnXin XLab, the activity involves the exploitation of CVE-2026-26980 (CVSS score: 9.4), an...
The Alert Firehose Finally Meets Its Match
Ask a cybersecurity pro about Network Detection and Response (NDR) and you might still hear “Noisy,” “Too much data.” But ask the teams running NDR that includes agentic AI capabilities and you’ll hear they’re actually using it to...
Lazarus Deploys RemotePE Memory-Only RAT Against Financial and Crypto Firms
Cybersecurity researchers have shed light on a cross-platform malware called RemotePE that has been put to use by the North Korea-linked Lazarus Group in attacks targeting financial and cryptocurrency organizations. RemotePE, per NCC Group subsidiary Fox-IT, is part...
TrapDoor Supply Chain Attack Spreads Credential-Stealing Malware via npm, PyPI, and CratesIO
A new coordinated cross-ecosystem software supply chain attack campaign has targeted npm, PyPI, and Crates.io to distribute credential-stealing malware. The campaign, codenamed TrapDoor, spans more than 34 malicious packages across over 384 versions. The earliest...
npm Adds 2FA-Gated Publishing and Package Install Controls Against Supply Chain Attacks
GitHub has rolled out new controls for npm to improve the security of the software supply chain, giving maintainers the ability to explicitly approve a release prior to the packages becoming publicly available for installation. Called staged publishing, the feature is...
About Us
CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.