
ToddyCat-Linked Umbrij Malware Abuses OAuth to Access Gmail via Google API
The threat actor known as ToddyCat has been attributed to a new malware called Umbrij that’s designed to gain surreptitious access to a victim’s email correspondence via the Google API. “In this campaign, the attackers focused their attention on...
Identity Lifecycle Management Wasn’t Built for AI Agents
Identity lifecycle management was architected around a person with an employment record, a manager, and a departure date. AI agents have none of those. As autonomous principals proliferate across enterprise environments, the governance model built for humans develops...
AI Agent Exploits Langflow RCE to Automate Database Ransomware Attack
Security firm Sysdig says it has found what it believes is the first ransomware attack run from start to finish by an AI agent. Its Threat Research Team calls the operator JADEPUFFER and says a large language model handled the whole job: breaking in, stealing...
FortiBleed Credential Theft Linked to INC and Lynx Ransomware Operations
The recently discovered financially-motivated FortiBleed campaign has been attributed to INC and Lynx ransomware operations, indicating that the verified, stolen credentials were intended for follow-on intrusions. “An operator tied to FortiBleed’s...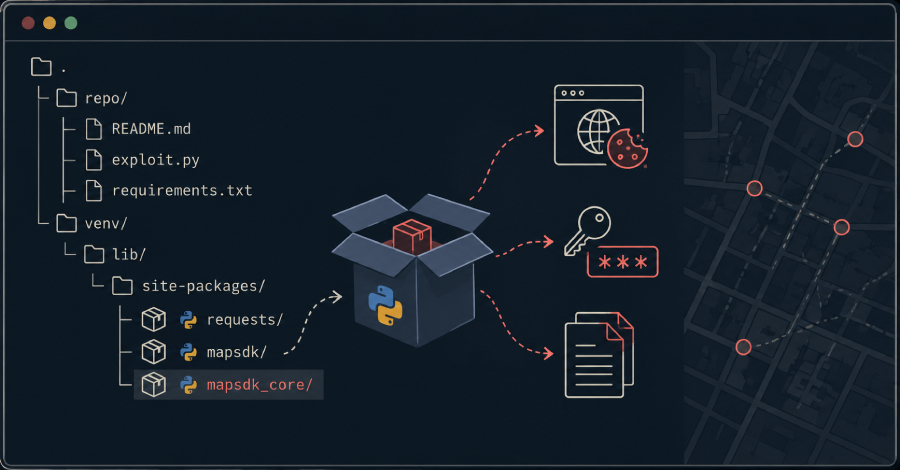
New ChocoPoC RAT Targets Vulnerability Researchers via Fake PoC Exploit Repos
Attackers are hiding a data-stealing trojan inside fake exploit code aimed at the people who hunt bugs for a living. The malware, called ChocoPoC, travels in Python proof-of-concept (PoC) repositories on GitHub that claim to exploit hot new CVEs. Run one, and it...
About Us

CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.
