Attackers Compile khunt Inside Oracle to Turn SQL Injection Into Windows SYSTEM Access
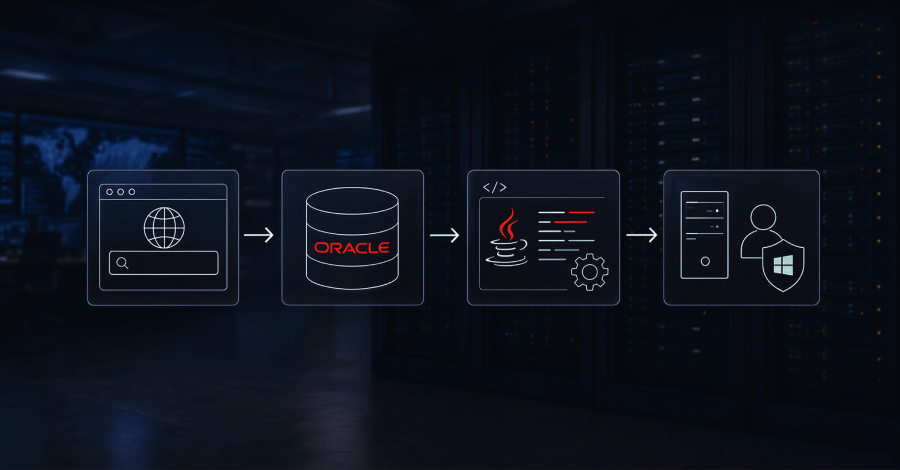
Attackers broke into an organization’s Oracle database through a SQL injection flaw in a public-facing web application, then installed a post-exploitation toolkit without writing an executable to disk. They fed Java source code to the database, let Oracle...
AWS, Google, and Vercel Agent Flaws Let Attackers Trigger Tools Without Running the Model
Security flaws in agent infrastructure from Amazon Web Services (AWS), Google, and Vercel let untrusted or forged instructions reach an agent’s tools with no check that a model turn had authorized them. In several of the attack paths, the model never ran at all,...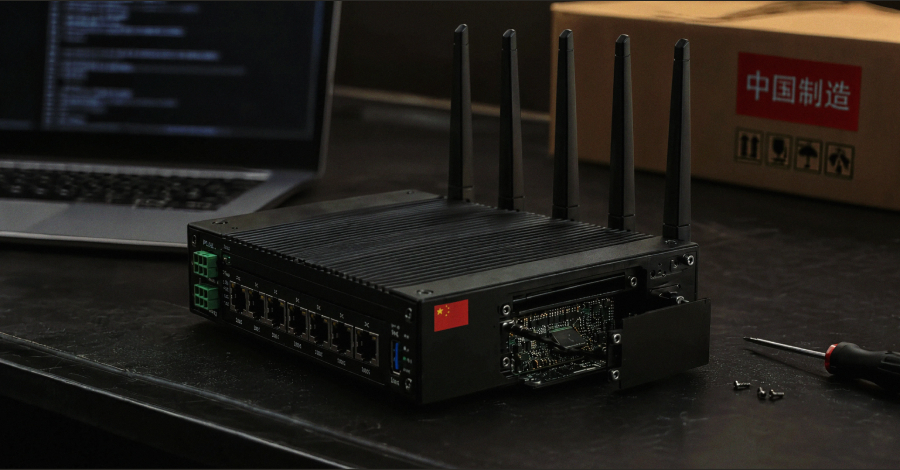
Chinese-Made Zbtlink Routers Ship With Backdoor That Opens Unauthenticated Root Shells
Cybersecurity researchers have disclosed details of a “factory-shipped backdoor” implanted in at least 20 Chinese router models from Zbtlink. According to a new report from VulnCheck, the implant appears in all 21 firmware images currently available from...
Ransom Cartel Creator Gets 16 Years in Prison for Operating Ransomware-as-a-Service
A federal judge in Alexandria, Virginia, sentenced Maksim Silnikau to 16 years in prison on August 5 for creating and running Ransom Cartel, the ransomware-as-a-service operation he stood up in 2021. Between 2021 and 2023, Ransom Cartel conspirators attacked at least...
About Us
CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.