
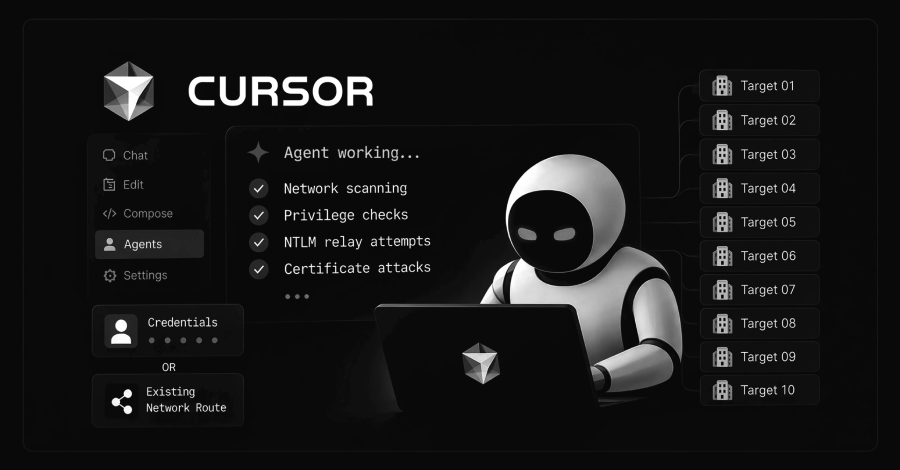
Aurora Ransomware Operators Use Cursor AI in Attacks Against 10 Targets
Threat actors associated with Aurora (aka Aur0ra) ransomware have been observed using SpaceX’s artificial intelligence (AI)-powered coding assistant Cursor to break into target networks, according to findings from CloudSEK and Gambit Security. The two...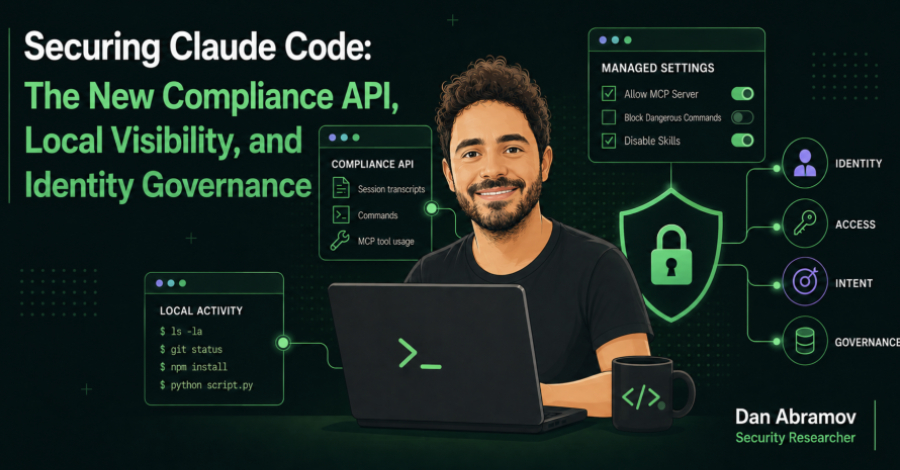
Securing Claude Code: The New Compliance API, Local Visibility, and Identity Governance
Claude Code reads files, runs shell commands, invokes MCP tools, and acts through the credentials available on a developer’s machine. Anthropic’s new Compliance API endpoints give security teams their clearest view yet into that activity. They also expose a larger...
China-Linked Fire Ant Hijacks Cisco Routers to Steal Credentials and Blind Security Logs
A China-nexus cyber espionage actor tracked as Fire Ant has expanded a long-running campaign beyond VMware hypervisors to compromise Cisco IOS XR routers, Terminal Access Controller Access-Control System (TACACS) servers, and Linux management hosts used to route,...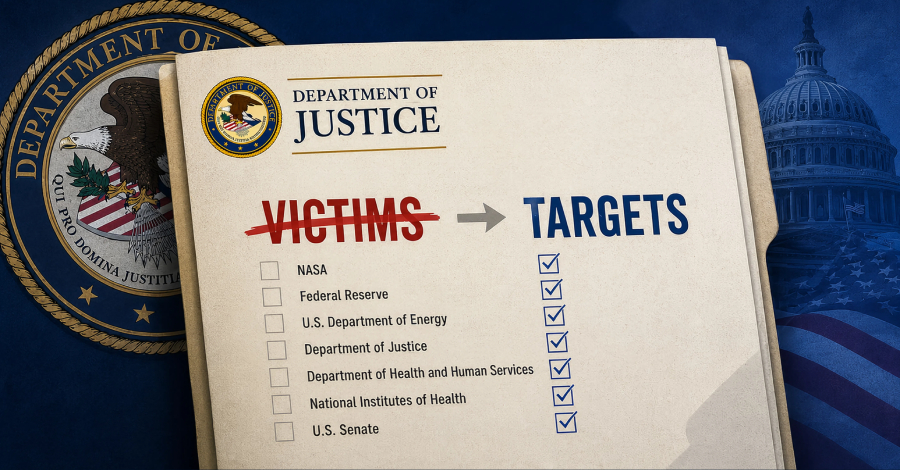
DoJ Corrects China Hacking Claim, Says U.S. Agencies Were Targets, Not Victims
The U.S. Department of Justice (DoJ) on Friday corrected a previously issued press statement that several of its agencies were victims of attacks carried out by Chinese threat actors, instead now pointing out that they were among those targeted. Last week, the DoJ...
About Us

CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.
