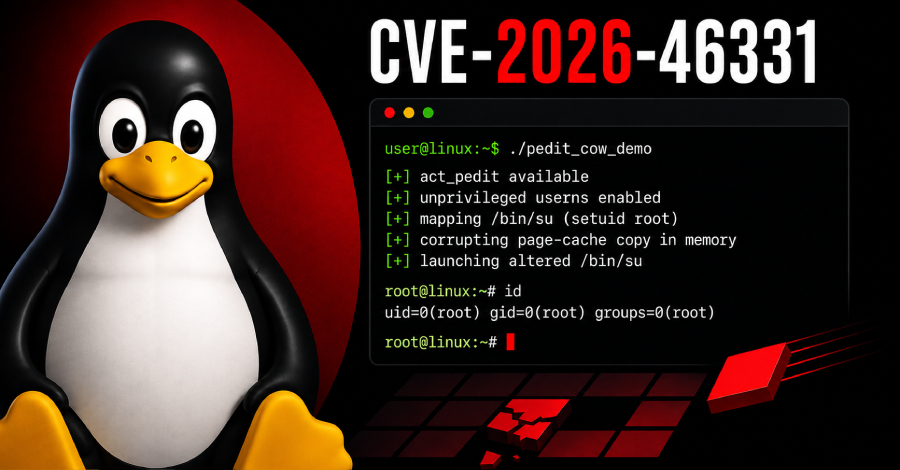
New Linux pedit COW Exploit Enables Root Access by Poisoning Cached Binaries
A flaw in the Linux kernel’s traffic-control subsystem can let a local unprivileged user gain root on affected systems. CVE-2026-46331, nicknamed “pedit COW,” is an out-of-bounds write in the packet-editing action (act_pedit) that corrupts shared...
CISA Adds Exploited PTC Windchill RCE Flaw to KEV as Web Shell Attacks Continue
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added a critical remote code execution vulnerability impacting PTC Windchill PDMlink and PTC FlexPLM enterprise Product Data Management (PDM) and Product Lifecycle Management (PLM) software...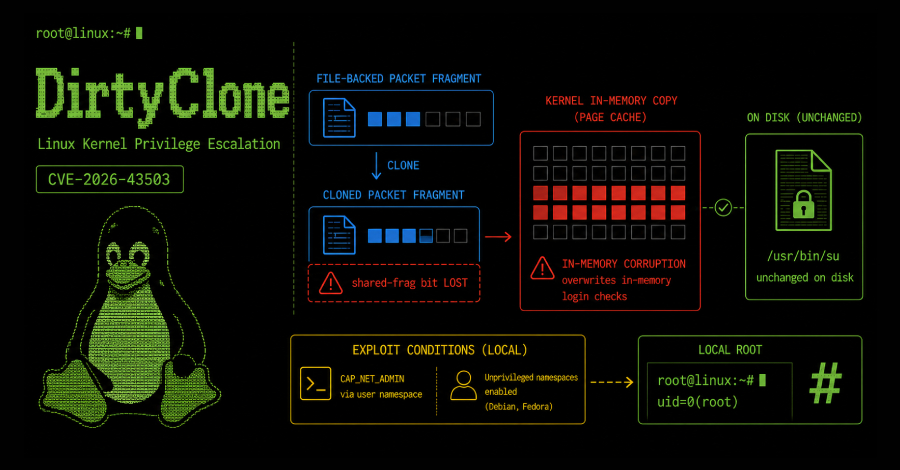
New DirtyClone Linux Kernel Flaw Lets Local Users Gain Root via Cloned Packets
DirtyClone is a new Linux kernel privilege escalation in the DirtyFrag family. JFrog Security Research published a working exploit walkthrough for the flaw on June 25, the first public demonstration for this variant. Tracked as CVE-2026-43503 (CVSS 8.8), it lets a...
Guardian Agents: The Next Layer of Identity Governance
AI agents are moving through enterprise environments, inheriting permissions, traversing systems, and executing decisions at machine speed with minimal oversight. The identity infrastructure built to govern human access wasn’t designed for autonomous actors, and...
About Us
CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.