SonicWall SMA Zero-Days Exploited Before Disclosure to Gain Root Access
A previously undocumented threat actor has been attributed to the exploitation of recently disclosed SonicWall Secure Mobile Access (SMA) 1000 series VPN appliances as zero-days prior their public disclosure since June 22, 2026. Cybersecurity company Volexity is...
New wp2shell WordPress Core Flaw Lets Unauthenticated Attackers Run Code
An anonymous HTTP request can run code on a WordPress site. The bug is in core, so a bare install with zero plugins is exploitable. Every 6.9 and 7.0 site was in range until Friday, when WordPress shipped 6.9.5 and 7.0.2 and enabled what it calls forced updates...
OpenSSL HollowByte Flaw Could Freeze Server Memory with 11-Byte TLS Requests
Eleven bytes will make an unpatched OpenSSL server set aside up to 131 KB of memory for a message that never arrives. On the glibc systems Okta tested, that memory is gone until the process restarts. OpenSSL shipped the HollowByte fix in June with no CVE, no advisory,...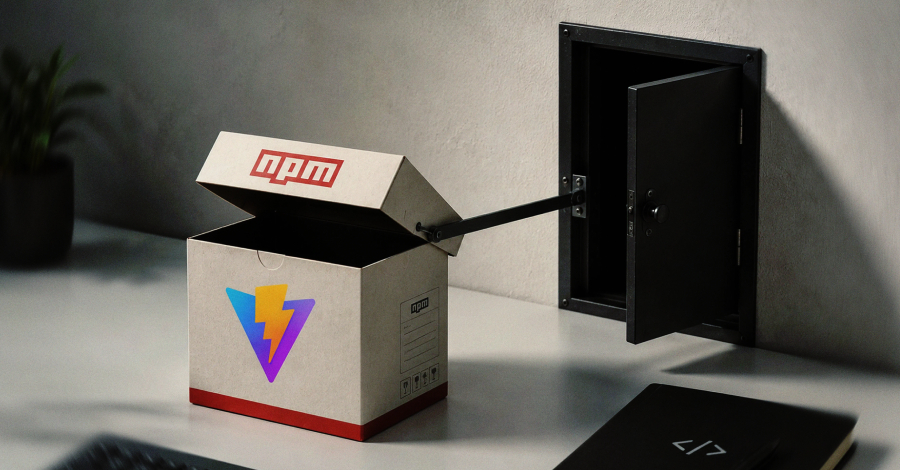
Seven Malicious Vite npm Packages Use Blockchain C2 to Deliver a RAT
Cybersecurity researchers have discovered a cluster of seven malicious npm packages targeting the Vite frontend tooling ecosystem as part of a software supply chain attack. The malicious package campaign, codenamed ViteVenom by Checkmarx, marks an expansion of...
About Us
CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.