
Acronis cPanel Backup Plugin Vulnerability Exploited in Targeted Attacks
Acronis has warned that a high-severity security flaw in its Backup plugin for cPanel and Web Host Manager (WHM) deployments has been exploited in the wild. The vulnerability, tracked as CVE-2026-87886 (CVSS score: 7.8), is described as a case of local privilege...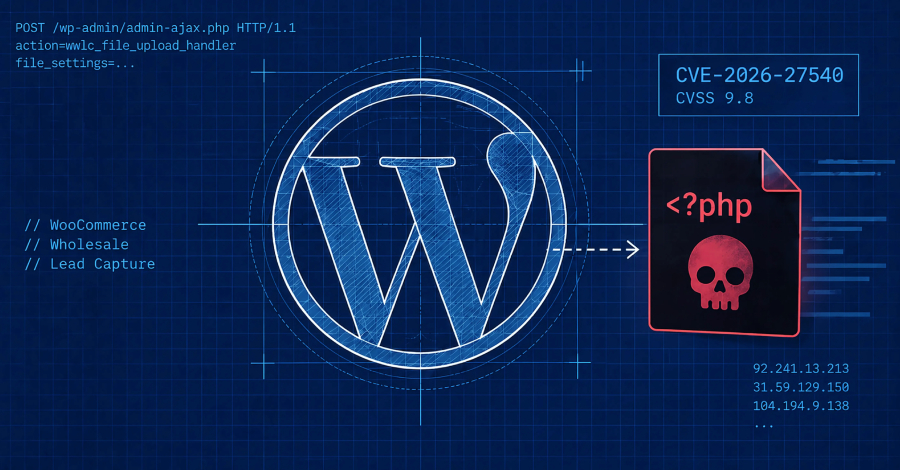
Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells
Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. “This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files,...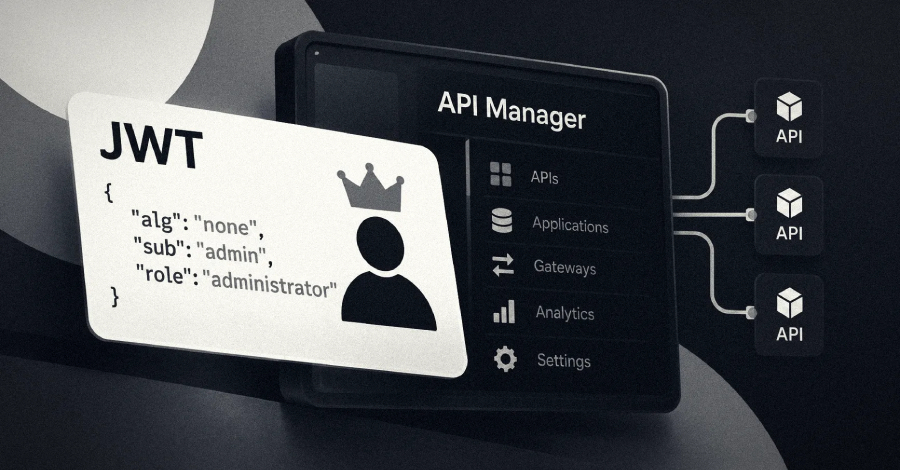
Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that...
KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334. Active since at least May 2025, the threat...
About Us

CISTCK Group is the most trusted partner for some of the world’s leading enterprises, innovators, SMEs and technopreneurs. We help businesses levitate their excellence through custom software development, UI/UX design, MVPs, Software Testing, and consultancy services.
